Compliance Overview
Controls Available In The Product
Company administrators can review organization identity, directory sync, privacy choices, approval history, and session records from the product.
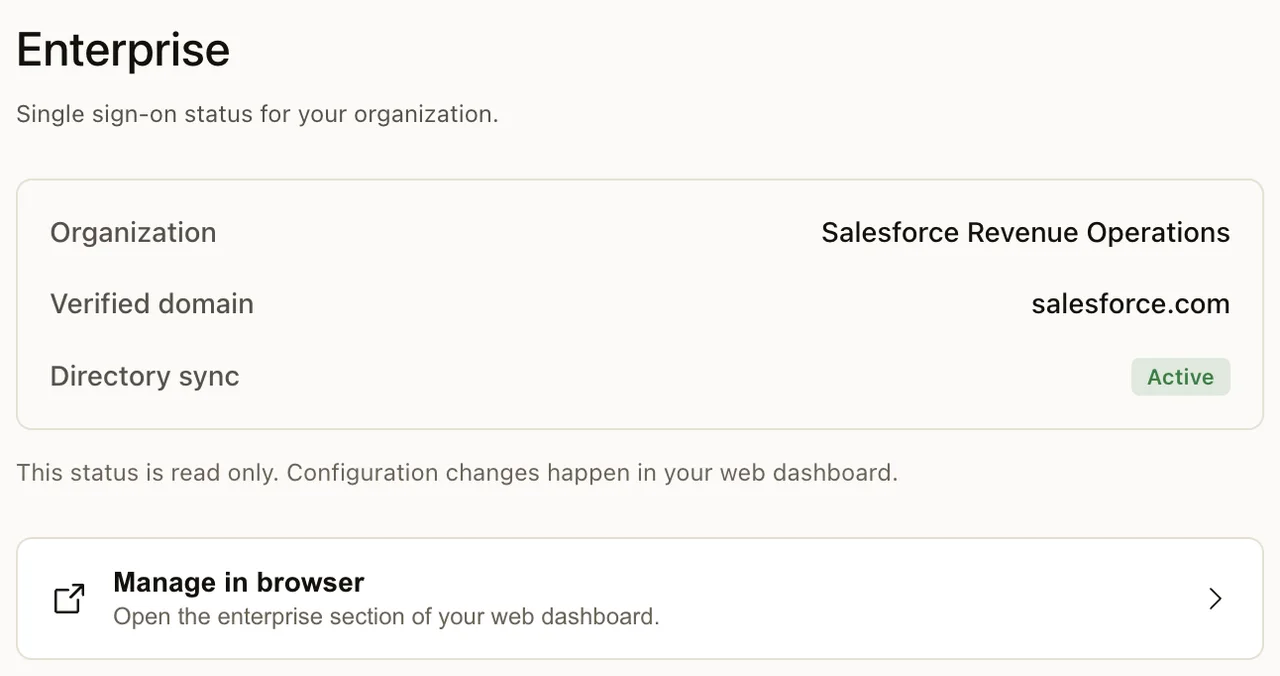
Where Neotask stands on security and privacy compliance, in plain language. We build to four frameworks, SOC 2, GDPR, ISO/IEC 27001, and HIPAA (for healthcare customers, under a BAA). For technical detail see Trust & Security; for your data rights see Data Privacy & Your Rights.
SOC 2
Neotask has built its controls to the SOC 2 Trust Services Criteria, Security, Availability, Confidentiality, Privacy, and Processing Integrity. We maintain a complete control framework (access control, encryption and key management, change management, monitoring, incident response, backup/DR, vendor management, and more), each backed by working controls in our product and a documented evidence trail.
- Status: SOC 2 Type I readiness. Our controls are designed and implemented; a Type II observation period (controls operating over time) is the next step.
- Reports: A SOC 2 report is issued by an independent auditor. If you're evaluating Neotask and need our current report or readiness package, we can share it under NDA, contact [email protected].
GDPR & data protection
Optional session-data sharing is controlled in Settings → Privacy and Data.
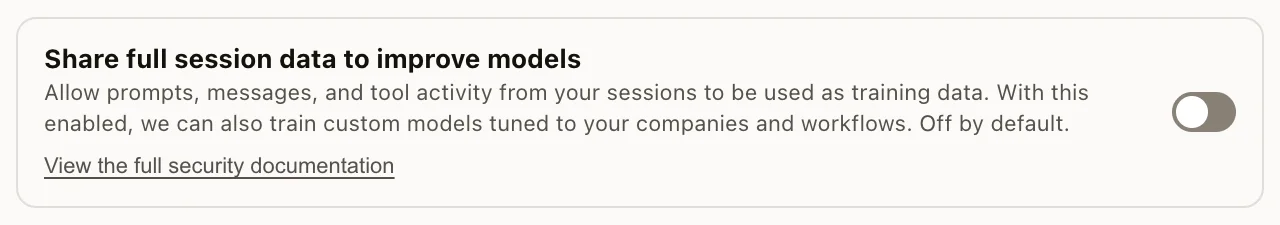
We process personal data in accordance with the EU General Data Protection Regulation (GDPR) and apply the same protections globally:
- Lawful, minimal processing, we collect only what we need to provide the service.
- Your rights, access, export (portability), correction, deletion, and the ability to object or withdraw consent. See Data Privacy & Your Rights.
- Subprocessors & transfers, we maintain a published subprocessor list and put data-processing terms in place with our vendors.
- Data Processing Agreement (DPA), a DPA is available to customers on request at [email protected].
- Breach handling, we maintain an incident-response process designed to meet GDPR's notification requirements.
ISO/IEC 27001
We operate an Information Security Management System (ISMS) aligned to ISO/IEC 27001:2022. We maintain a full Statement of Applicability covering all 93 Annex A controls, a risk register and treatment plan, and the management-system documentation the standard requires (context, leadership, planning, support, operation, performance evaluation, and improvement).
- Status: ISMS built and Stage 1-ready. ISO 27001 certification is granted by an accredited registrar after a Stage 1 (documentation) and Stage 2 (implementation) audit plus an operating period; we are preparing for that external audit. We are not yet certified.
- Documentation: Our ISMS scope, Statement of Applicability, and readiness package can be shared under NDA, contact [email protected].
HIPAA
Actions that require a person remain visible in the approval record with the requested operation and review controls.
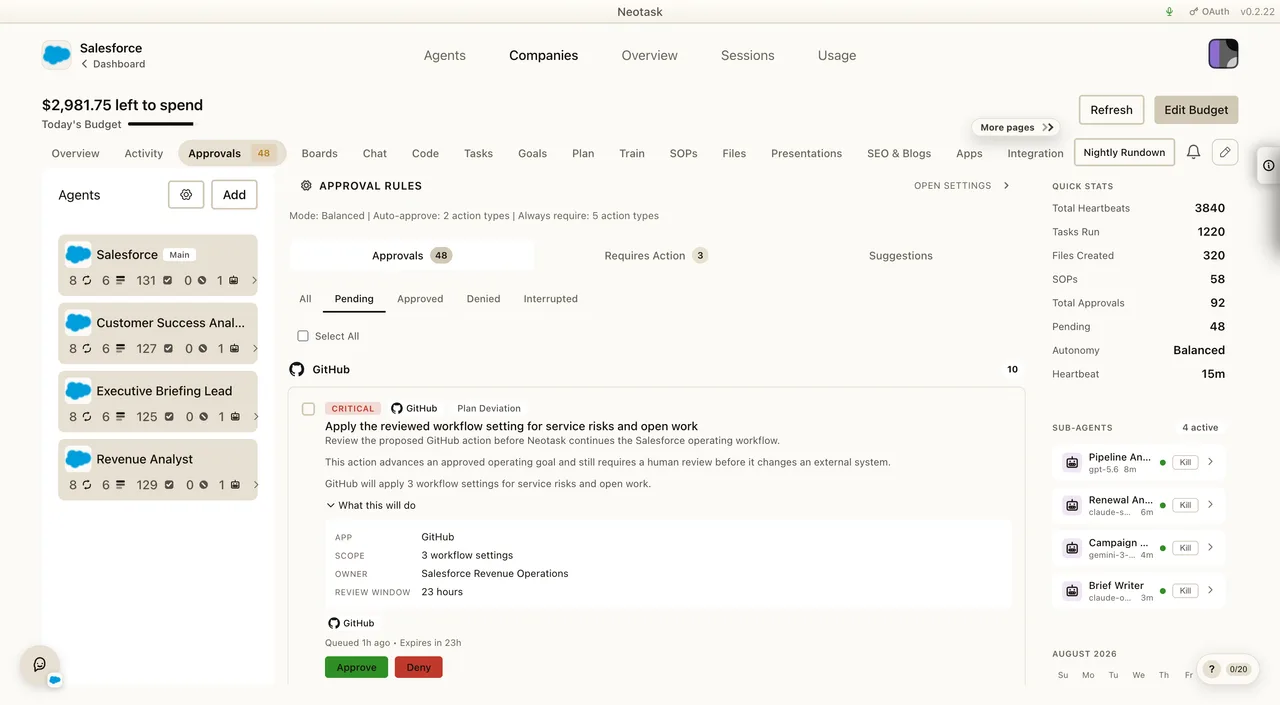
For healthcare customers, Neotask operates as a HIPAA Business Associate and will sign a Business Associate Agreement (BAA). The HIPAA Security Rule safeguards (access control, encryption at rest and in transit, audit logging, integrity, transmission security, automatic logoff, and minimum-necessary handling) are built into the product. When a healthcare customer is onboarded under a BAA, their protected health information (PHI) is handled in a dedicated, isolated, BAA-covered environment with a BAA-covered AI provider, it never flows to non-BAA subprocessors.
- Status: HIPAA-aligned Business Associate posture, available to healthcare customers under a signed BAA. There is no such thing as "HIPAA certified", HIPAA is enforced by regulation (OCR) and by the BAA contract, not by a certificate.
- To engage: contact [email protected] to start a BAA and healthcare onboarding.
Hosting & subprocessors
We rely on established infrastructure and service providers, each with their own security/compliance programs. The current list of subprocessors that may process customer data is published on the Subprocessors page and is kept up to date; material changes are communicated per your agreement.
How to request documentation
| You need | Contact | Notes |
|---|---|---|
| SOC 2 report / readiness package | [email protected] | Shared under NDA |
| ISO 27001 ISMS scope / SoA / readiness | [email protected] | Shared under NDA |
| HIPAA BAA + healthcare onboarding | [email protected] | For healthcare customers |
| Data Processing Agreement (DPA) | [email protected] | For customers / prospects |
| Security questionnaire | [email protected] | We'll complete standard questionnaires |
| Privacy / data-rights request | [email protected] | See Data Privacy & Your Rights |
This page describes our compliance posture; it is not itself a certification. SOC 2 reports are issued by an independent CPA firm; ISO/IEC 27001 certification is issued by an accredited registrar; GDPR compliance is demonstrated through our documentation and practices; and HIPAA is enforced by regulation and by the Business Associate Agreement, we can evidence each on request.