Trust & Security
Product Controls
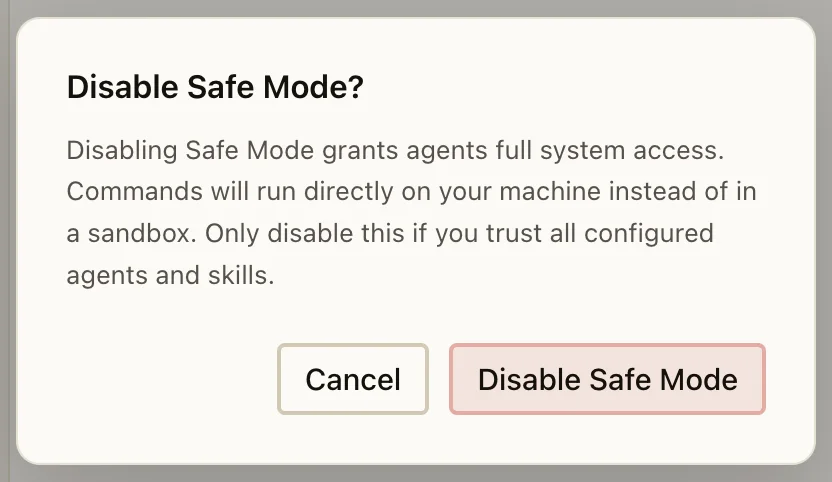
Use Settings → Privacy and Data for data choices, Settings → Permissions for Safe Mode, and Approvals for actions waiting on review.
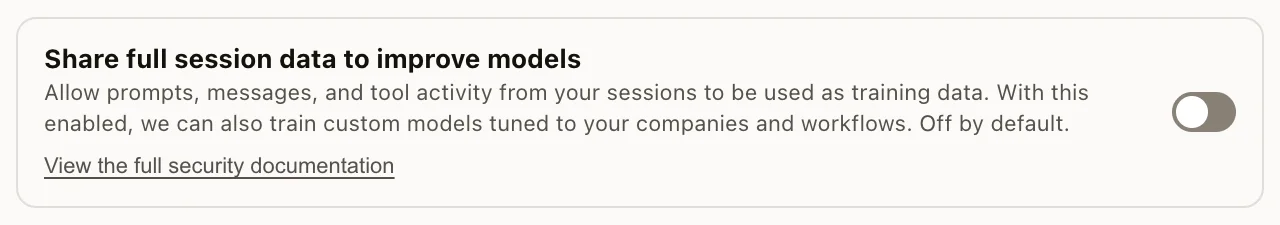
How Neotask protects your data. This page summarizes our security posture for customers and prospects. For our formal compliance status and how to request audit reports, see Compliance Overview. For data-protection rights, see Data Privacy & Your Rights.
Our security principles
- Your data is kept secure, durable, and consistent. Your data is stored in a secure, managed cloud environment with automated, regularly-tested backups; any copy cached on your device for offline use is encrypted and kept in sync, so you always see accurate, up-to-date information.
- Encrypt everywhere. Sensitive data is encrypted in transit (TLS) and at rest. Credentials, tokens, and provider keys are encrypted at the field level before storage.
- Least privilege + tenant isolation. Every request is authenticated and scoped to your account from a verified token, never from client-supplied identifiers. One tenant can never see another's data.
- Private by default. Telemetry and error monitoring run with personal data collection disabled and redaction on by default.
Data protection
| Area | What we do |
|---|---|
| Encryption in transit | All API and gateway traffic uses TLS. Plaintext transport is refused. |
| Encryption at rest | AES-256-GCM field-level encryption for credentials, OAuth tokens, provider keys, and other sensitive records, with versioned keys and backward-compatible key rotation. |
| Access control | Token-based authentication, role-based access within an account, and HMAC-signed requests (nonce + timestamp) for device and service calls. |
| Secrets management | No hardcoded secrets; production secrets are required at startup (the service fails closed if a required secret is missing) and are never logged. |
| Audit logging | Privileged and security-relevant actions are recorded to an append-only, tamper-evident audit log. |
| Monitoring | Error and availability monitoring with health checks and alerting; personal data is excluded from telemetry by default. |
Infrastructure & hosting
- Hosted on established cloud providers with their own SOC 2 / ISO programs (database, application platform, object storage).
- Network hardening on the database tier (restricted access, encrypted connections).
- Backups with a tested restore procedure and a documented disaster-recovery plan.
Secure development
Safe Mode requires an explicit confirmation before broader machine access is enabled.
- Code review and change-management controls before changes reach production.
- Dependency and vulnerability management.
- A documented Secure SDLC and incident-response plan, with a defined breach-handling process.
AI processing
Neotask routes AI requests through our gateway to model providers (see the Subprocessors list). We minimize what is sent, do not use your private content to train our own models, and document the providers that may process prompt content so you can make an informed choice.
Reporting a security issue
If you believe you've found a vulnerability, contact [email protected]. Please do not publicly disclose it until we've had a chance to investigate and remediate.